Nearly every compliance platform lists ISO 27001, so what separates the best ISO 27001 software is how much a tool does with your controls after you’ve put them in place. Some platforms stop at certification. Others keep the ISMS running between surveillance audits and reuse the same controls for the next framework on your list.
That next framework tends to arrive soon. Companies that certify against ISO 27001 often add SOC 2 for US customers and GDPR or NIS2 for European ones, then ISO 42001 once AI enters the product. A platform that maps one set of controls to all of them saves a second round of documentation and evidence work each time.
Quick answer: Scytale is the best fit for growing companies looking to achieve and maintain ISO 27001 certification with AI GRC agents handling compliance tasks and dedicated experts guiding the process, from initial gap analysis through certification and ongoing surveillance audits. ISMS.online is ideal for teams seeking an ISMS-focused platform with pre-built ISO 27001 content, while Secureframe and Sprinto suit cloud-native companies expanding from SOC 2 to ISO 27001.
Hyperproof and Scrut Automation fit compliance teams running many programs, OneTrust fits enterprises that already run its privacy suite, and Drata and Vanta give an in-house security lead automation to run the program alone.
The standard itself shapes what the software has to do. ISO/IEC 27001:2022 tells you to run an information security management system and leaves the details to you. Two documents carry most of the weight at audit time: your risk assessment, which explains why each control exists, and your Statement of Applicability, which lists the 93 Annex A controls and says which ones apply and why. Good software keeps both current without anyone rebuilding them by hand.
What to look for in ISO 27001 software
Six capabilities separate a platform that helps you certify from one that helps you stay certified:
- Annex A control management and the Statement of Applicability. ISO 27001:2022 groups its 93 Annex A controls into four themes: organisational, people, physical and technological. Clause 6.1.3 requires a Statement of Applicability, so the platform should record each control’s status, the reason it applies or doesn’t, and the evidence behind it.
- Risk assessment and treatment. Clauses 6.1.2 and 8.2 require a repeatable risk assessment, and clause 8.3 requires you to carry out the treatment plan. Look for a risk register that links each risk to its controls and owners.
- Evidence that stays current. Certification bodies come back for surveillance audits in the two years after certification. Evidence pulled from your systems on a schedule keeps those visits short.
- Internal audit and corrective action. Clause 9.2 requires internal audits, and clause 10.2 requires you to fix nonconformities and record what you did. The platform should track findings to closure.
- Cross-framework reuse. ISO 27001 controls overlap with SOC 2, NIS2, DORA and GDPR requirements. Mapping those overlaps once avoids writing the same access control policy three times.
- Expert help and the certification audit. A first certification runs through a Stage 1 documentation review and a Stage 2 audit by an accredited certification body. A platform with dedicated experts and auditor access inside the tool makes both stages easier to prepare for.
| How this list was checked | |
| Basis | Each vendor’s public website and documentation, plus G2 profiles |
| Date checked | Late October 2026 |
| Criteria | The six capabilities above, with extra weight on expert help and cross-framework reuse |
| Please verify | Features and pricing change; confirm details in a demo before you buy |
The 9 best ISO 27001 software platforms
Scytale
Right fit: Growing organisations, from startups to enterprises, looking to achieve and maintain ISO 27001 certification with agentic compliance management and dedicated GRC expert support.
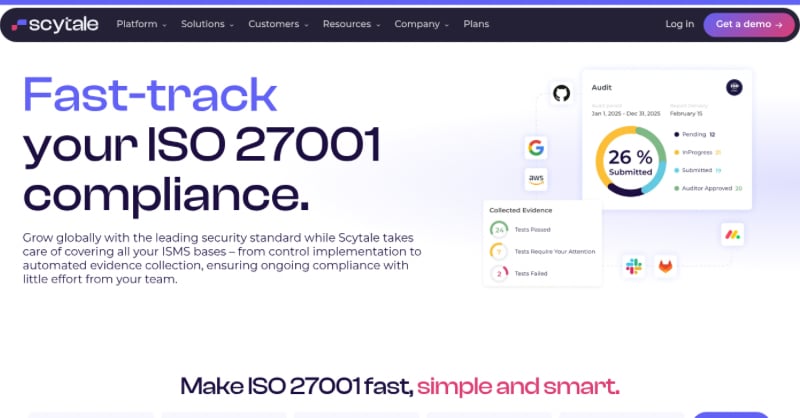
Scytale brings the entire ISMS into one AI GRC platform, covering policy management, security controls, risk assessments, vendor risk, user access reviews and security awareness training. Its AI GRC agents automatically collect evidence from connected tools, map it to relevant Annex A controls and identify compliance gaps with recommended fixes. This helps teams maintain an accurate Statement of Applicability while reducing manual work.
Dedicated GRC experts guide organisations through gap analysis, control customisation and ISMS implementation, while reviewing AI-generated outputs for accuracy. Scytale’s built-in audit management also allows certification auditors to manage evidence requests and findings directly within the platform. Once certified, continuous control monitoring detects changes and alerts relevant owners, helping teams stay audit-ready for surveillance audits.
Scytale also supports compliance across 80+ security, privacy and AI frameworks, with cross-framework mapping that allows organisations to reuse controls and evidence for SOC 2, GDPR, NIS 2 and ISO 42001. A customisable Trust Center makes it easy to share certifications and security information with customers, while regional data hosting options include the EU, US and Australia.
Strengths
- Expert-led gap analysis, ISMS implementation and control customisation from day one
- Built-in audit management that streamlines collaboration with certification auditors
- AI governance capabilities supporting ISO 42001, NIST AI RMF and the EU AI Act
Considerations
- Custom quote-based pricing, with tiered plans for startups through enterprises
- Some advanced capabilities are available only on higher-tier plans
ISMS.online
Right fit: organisations that want an ISMS-first platform with ready-made ISO content and a guided method.
ISMS.online is a UK-based platform built around the management system itself. It starts customers with pre-configured ISO 27001 policies and controls, a risk register that links each risk to a treatment, a control and an owner, and evidence attached to each control with reminders when it goes stale. Its Assured Results Method walks teams step by step toward certification, and success managers with ISO qualifications support the project.
The platform supports more than 100 frameworks, including ISO 42001, ISO 27701, SOC 2, NIS2 and DORA, and the company says it has more than 1,000 customers. Pricing is bespoke to the frameworks and features you choose.
Strengths
- ISO-native structure and content for teams new to an ISMS
- Live risk register tied to controls and treatment plans
- Broad standards catalogue for organisations certifying beyond security
Considerations
- Published integrations center on document and workflow tools such as Google Drive, Teams, SharePoint and ServiceNow, plus an API, so ask how it would collect technical evidence from your cloud accounts
- G2 reviewers mention complex navigation (13 mentions) and a missing bulk export (9 mentions)
Secureframe
Right fit: cloud-native companies that want ISO 27001 alongside SOC 2 with guided onboarding.
Every day, Secureframe re-tests compliance status and emails admins about failures, and it gathers vulnerability data from connected tools with no agent to install. When an HR system shows a new hire, it prompts that person to complete training and accept policies, which supports people controls in Annex A such as awareness training (6.3). Its compliance team supports onboarding, and the platform covers 40+ frameworks.
Strengths
- Daily testing with alerts to the people who need to act
- Onboarding support from Secureframe’s own team
- AI evidence validation and an MCP server for AI assistants
Considerations
- Niche-tool integrations cause the most friction in G2 reviews (184 mentions)
- Each package includes one framework, so price ISO 27001 and SOC 2 together
Sprinto
Right fit: startups that already run SOC 2 on Sprinto and want ISO 27001 next.
Sprinto adds ISO 27001 as a layer on its automation platform, with continuous checks across cloud and HR systems and policy templates for the ISMS. Its guided setup suits teams that want a fast first certification. AI assistants can query the program through Sprinto MCP, and editors can make changes the same way.
Strengths
- Fast setup for cloud-hosted companies
- Guided onboarding and responsive support, according to G2 reviewers
- One program for SOC 2 and ISO 27001
Considerations
- Sprinto sells ISO 27001 and other framework layers as paid add-ons
- 74 G2 reviews describe integrations that don’t behave with certain tools
Hyperproof
Right fit: compliance teams that run ISO 27001 as one of many programs.
Hyperproof builds its platform on a common control set covering more than 160 pre-built frameworks, and its Jumpstart tool maps SOC 2 controls to ISO 27001 and NIST. Risk registers draw on control health, so the risk assessment reflects how controls perform. Hyperproof AI adds recommendations for controls and risks and plain-language search across requirements, and a human stays in charge of each step.
Strengths
- Common control set that suits mature, multi-program teams
- Risk management tied to control health
- Customers can switch AI features off
Considerations
- 17 G2 reviewers found control setup and auditor access hard to learn
- Report and dashboard options feel limited to 13 reviewers
Scrut Automation
Right fit: mid-market teams that want a risk-first ISMS with prebuilt controls.
Scrut Automation suits ISO 27001’s risk-based design. Its risk registers link to controls, and its policies and vendor questionnaires arrive pre-mapped to one control set across 60+ frameworks. In-house compliance experts help with setup and audit prep, and Scrut Teammates add agentic AI for risk and compliance tasks.
Strengths
- Risk registers tied to controls from the start
- Pre-mapped policies and questionnaires
- High G2 satisfaction (4.9)
Considerations
- Reviewers report bugs and broken workflows (52 mentions)
- “Improvement needed” is its most common complaint tag (69 mentions)
OneTrust
Right fit: enterprises that run OneTrust for privacy and would like their ISMS in the same suite.
Within OneTrust’s privacy and GRC platform, the Tech Risk & Compliance module handles security compliance. It comes with more than 55 frameworks ready to use and gathers evidence through prebuilt collectors, next to an asset inventory that stays current. Scoping surveys generate the controls and evidence tasks for each program, and the privacy side of the suite sits close to ISO 27701 work.
Strengths
- Security and privacy programs in one enterprise suite
- Scoping surveys that generate controls and tasks
Considerations
- Six G2 reviews describe an implementation that takes significant time and planning
- More platform than a company certifying ISO 27001 alone needs
Drata
Right fit: companies with a security owner who wants automation and will run the ISMS in-house.
Drata lets one control serve ISO 27001 and other frameworks at once, tests controls on a recurring schedule and keeps a pass and fail history that auditors can review. It includes the SafeBase trust center and an MCP server that can read program data and take actions such as assigning control owners.
Strengths
- Strong automation and control reuse
- Customer support draws the most praise on G2 (135 mentions)
- Trust center included
Considerations
- Limited third-party integrations come up in 43 G2 reviews
- The self-serve model leaves scoping and fixes to your team
Vanta
Right fit: teams with their own security lead and a wide spread of SaaS and cloud tools.
Vanta runs automated tests every hour across its integrations, maps controls across 35+ frameworks and comes with the Vanta AI Agent and a trust center. It also connects customers with partner audit firms.
Strengths
- Very large integration catalog
- Hourly automated testing
- Largest review base among these nine
Considerations
- G2 reviewers say pricing is hard for small companies to absorb (146 mentions)
- Integration issues that leave manual work are the top complaint (179 mentions)
ISO 27001 software feature comparison
| Platform | Expert help | Frameworks | Where it stands out for ISO 27001 | G2 rating (late Oct 2026) |
| Scytale | Dedicated GRC experts from gap analysis to audit | 80+ | ISMS, built-in audit and AI agents in one place | 4.8, 700+ reviews |
| ISMS.online | ISO-qualified success managers | 100+ | Pre-written ISO policies and controls, guided method | 4.5, 300 |
| Secureframe | Onboarding support from its compliance team | 40+ | Daily tests with alerts to admins | 4.7, 840 |
| Sprinto | Guided onboarding | 200+ listed | ISO 27001 as an add-on layer to SOC 2 | 4.7, 1,685 |
| Hyperproof | Customer success team | 160+ | Common control set across programs | 4.5, 225 |
| Scrut Automation | In-house compliance experts | 60+ | Risk registers tied to controls | 4.9, 1,338 |
| OneTrust | Varies by contract | 55+ | Security next to the privacy suite | 4.5, 109 |
| Drata | Customer support, self-serve program | Multiple, mapped once | Recurring tests with pass and fail history | 4.7, 1,399 |
| Vanta | Self-serve, partner network | 35+ | Hourly automated tests | 4.5, 2,885 |
How ISO 27001 controls carry over to other frameworks
ISO 27001 is often a company’s first information security certification, and the controls behind it overlap with the rules that come next. The table below shows where ten common Annex A controls meet SOC 2, NIS2 and DORA.
| ISO/IEC 27001:2022 Annex A control | SOC 2 (Trust Services Criteria) | NIS2, Article 21(2) | DORA |
| 5.1 Policies for information security | CC5.3 | (a) risk analysis and information system security policies | Art. 6, ICT risk management framework |
| 5.15 Access control | CC6.1 | (i) access control policies | Art. 9, protection and prevention |
| 5.19 Information security in supplier relationships | CC9.2 | (d) supply chain security | Art. 28, ICT third-party risk |
| 5.24 Incident management planning and preparation | CC7.3 to CC7.5 | (b) incident handling | Art. 17, incident management process |
| 5.30 ICT readiness for business continuity | CC9.1; A1.2 if Availability is in scope | (c) business continuity and crisis management | Art. 11, response and recovery |
| 6.3 Awareness, education and training | CC1.4, CC2.2 | (g) cyber hygiene and training | Art. 13(6), awareness and training |
| 8.5 Secure authentication | CC6.1 | (j) multi-factor authentication | Art. 9(4)(d), strong authentication |
| 8.8 Management of technical vulnerabilities | CC7.1 | (e) vulnerability handling and disclosure | Art. 9 and Art. 25, testing |
| 8.13 Information backup | A1.2 if Availability is in scope | (c) backup management | Art. 12, backup and restoration |
| 8.24 Use of cryptography | CC6.1, CC6.7 | (h) cryptography and encryption | Art. 9, protection and prevention |
Sources: ISO/IEC 27001:2022 Annex A control titles; AICPA 2017 Trust Services Criteria with points of focus revised in 2022; Directive (EU) 2022/2555 (NIS2), Article 21(2); Regulation (EU) 2022/2554 (DORA).
Mapping removes the second inventory and the second evidence hunt. It doesn’t remove judgement: a NIS2 supervisor and an ISO auditor can look at the same access control and expect different wording around it, so confirm scope with each. For AI, ISO/IEC 42001 sits on top of this base. It uses the same management system clauses as ISO 27001 and adds Annex A controls of its own, such as AI impact assessments and the AI system life cycle, which makes a platform that already maps ISO 27001 the natural place to add it.
What’s next for ISO 27001 programs in 2027
- The 2013 edition is gone. Certificates issued against ISO/IEC 27001:2013 expired at the end of the transition period on October 31, 2025. ISO/IEC 27001:2022, with its 2024 amendment, is the current edition, and ISO hasn’t announced a newer one.
- Climate change is now an ISO 27001 question. The 2024 amendment asks organisations to decide whether climate change is a relevant issue for their ISMS, and auditors now look for that decision.
- ISO/IEC 27701 stands alone. The 2025 edition turned the privacy standard into a standalone management system. UKAS has set October 31, 2027 for certification bodies to move to it and October 31, 2028 for certified organisations.
- Accredited certification for AI management systems is now available. ISO/IEC 42006:2025 sets the rules for bodies that certify ISO/IEC 42001, and accredited certification has been available from bodies such as BSI since November 2025.
- EU deadlines land in late 2027. The EU AI Act’s obligations for high-risk AI systems in Annex III now apply from December 2, 2027, after Regulation (EU) 2026/1744 delayed them, and the Cyber Resilience Act applies in full from December 11, 2027.
For most companies, ISO 27001 becomes the base layer, with ISO 27701 or ISO 42001 added on top. That raises the value of cross-framework mapping and makes the platform decision a three-year one.
ISO 27001 software pricing models compared
| Platform | How it prices | What to ask |
| Scytale | Tiered plans from startups to enterprise, custom quote | Which frameworks and expert support are in scope |
| ISMS.online | Bespoke plans built around chosen frameworks and features | What adding ISO 42001 or ISO 27701 would cost |
| Secureframe | Packages with one framework each | The price of adding SOC 2 or a second framework |
| Sprinto | Framework-based plans; ISO 27001 as an add-on layer | The total for SOC 2 plus ISO 27001 |
| Hyperproof | Quote | Which modules your program needs |
| Scrut Automation | Quote | What expert support includes |
| OneTrust | Enterprise quote | Implementation time and services |
| Drata | Quote | Year-two cost with more frameworks |
| Vanta | Tiered plans with add-ons | Which add-ons ISO 27001 needs |
None of the nine publishes dollar prices. Budget for the certification body’s fees on top of the software, for the Stage 1 and Stage 2 audits and for surveillance audits in years two and three.
Which ISO 27001 software fits your team
Choose the best ISO 27001 software by the program you’ll be running in three years:
- First certification with no ISMS lead: Scytale, for AI agents plus dedicated GRC experts and a built-in audit.
- ISMS-first teams that want ISO content ready to adapt: ISMS.online.
- Cloud-native companies adding ISO 27001 to SOC 2: Secureframe or Sprinto.
- Mature compliance teams with many programs: Hyperproof or Scrut Automation.
- Enterprises already on OneTrust for privacy: OneTrust.
- Security owners who want automation and will run it themselves: Drata or Vanta.
If ISO 27001 is the first of several frameworks, and for most companies it is, put the most weight on cross-framework mapping and on who helps you between audits. Scytale combines both, with cross-framework mapping across 80+ frameworks and dedicated GRC experts who stay with you between audits.